n8n v3 update: no release yet, and two changes missing from the docs
n8n 3.0 is still unreleased, but its code lists two breaking changes the docs page doesn't: an enforced Content-Security-Policy and always-on workflow tags.
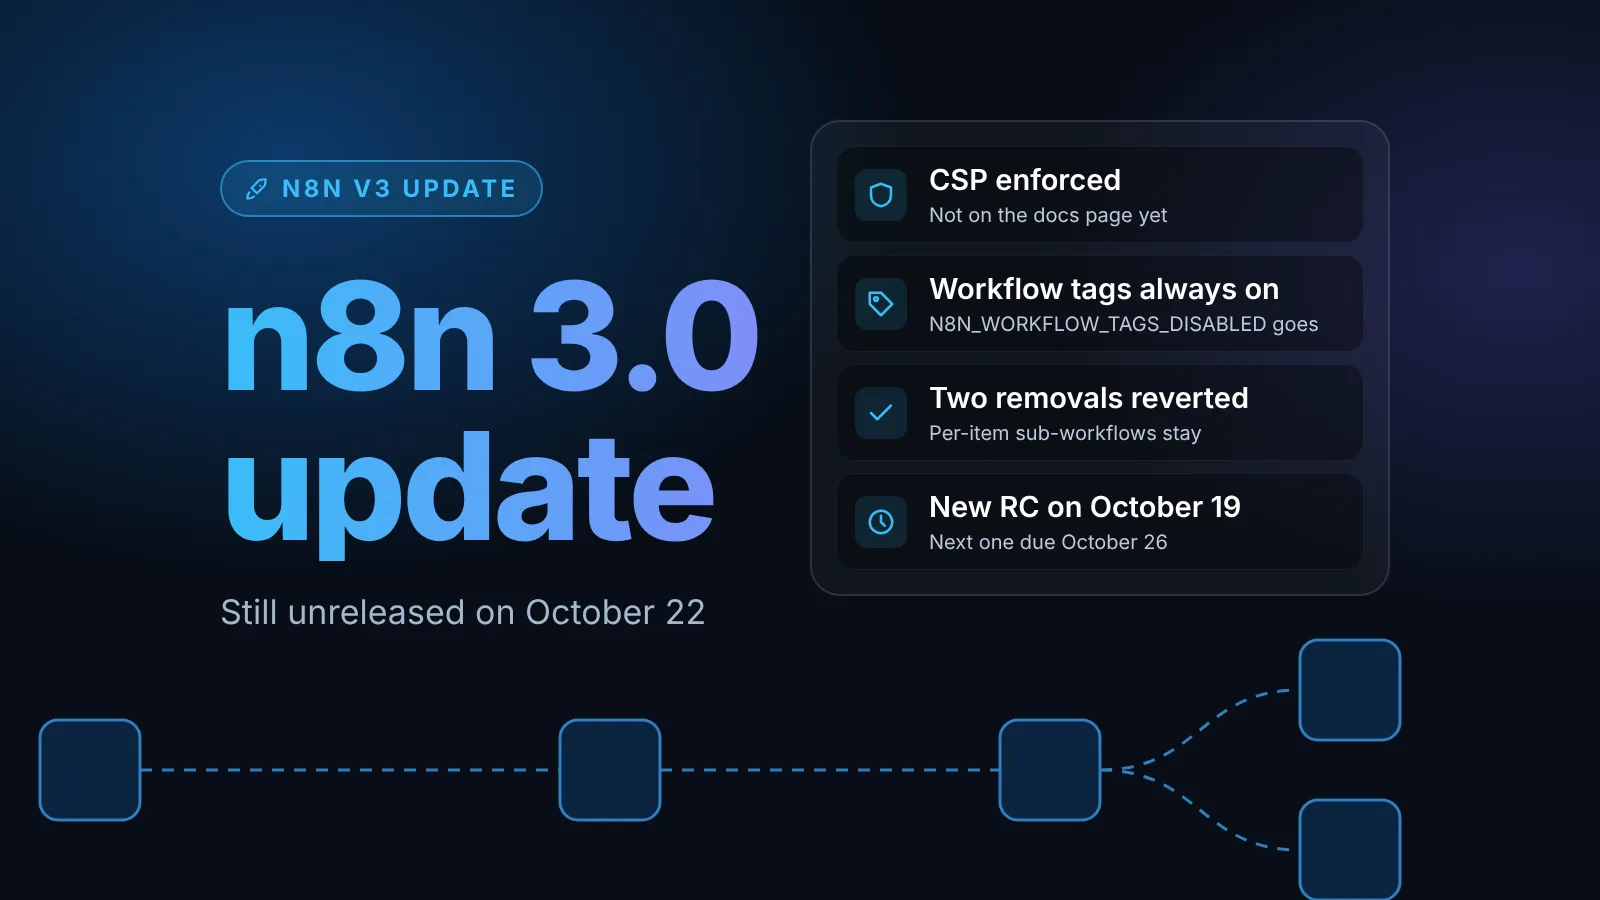
n8n 3.0 is still not released. On October 22, 2026, npm's stable version is 2.44.6 and the beta is 2.45.2, GitHub has no 3.x tag, and n8n's 3.0 breaking changes page still says it "is releasing soon." What's new since our 3.0 nightly test is a closer look at the 3.0 code. n8n's own engineering list of breaking changes includes two that the public page doesn't mention: n8n 3.0 enforces a Content-Security-Policy on its pages, and it removes the setting that hides workflow tags.
We confirmed both in today's nightly build. If you inject your own scripts into the n8n editor, or run with N8N_WORKFLOW_TAGS_DISABLED=true, plan for them.
The short version
- Release status: no 3.0 yet. n8n published a new weekly release candidate,
v3-rc-20261019.1, on October 19, and nightly builds continue. n8n's internal v3 development guide still targets "~October 2026." - No new breaking changes since October 18. The only 3.x-only commit since our test is a queue-mode bug fix (marked
no-changelog). - Not on the docs page: 3.0 switches the editor's Content-Security-Policy from report-only to enforced. In our test, 2.45.2 sent
Content-Security-Policy-Report-Only; the 3.0 nightly sent an enforcedContent-Security-Policy, on a fresh instance and on one upgraded from 2.45.2. - Also not on the docs page:
N8N_WORKFLOW_TAGS_DISABLEDis removed. Workflow tags are always on, and tags you had hidden reappear. - Dropped from the plan: two earlier 3.0 removals were reverted, so the Execute Sub-workflow node's per-item mode and the "Any workflow" caller policy stay.
Where n8n 3.0 stands on October 22
| What we checked | Result |
|---|---|
| npm dist-tags | stable 2.44.6, beta 2.45.2. No 3.x version. |
| GitHub tags | No n8n@3 tag. |
| Docker Hub | Daily v3-nightly images (the latest from October 22) and weekly v3-rc images (the latest v3-rc-20261019.1). |
| n8n's 3.0 breaking changes page | Last changed October 16, when n8n corrected "has been released" to "is releasing soon." |
| n8n's v3 development guide | Still says "~October 2026." |
The 3.x branch | No new breaking changes since October 18. |
The preview images still report a 2.x version: today's nightly prints 2.45.0 from n8n --version. Our nightly test explains how the 3.x branch and its images work.
The 3.0 changes the docs page doesn't list
The public page isn't n8n's only list. The repository keeps a BREAKING-CHANGES.md file, and its 3.0.0 section on the 3.x branch has eight entries. Six match the docs page. These two don't appear there.
n8n 3.0 enforces a Content-Security-Policy
A Content-Security-Policy (CSP) header tells the browser which scripts a page may run. n8n 2.x already sends one, but as Content-Security-Policy-Report-Only, which per n8n's file "reported violations but blocked nothing." In 3.0 it becomes an enforced Content-Security-Policy:
script-src 'nonce-...' 'strict-dynamic' 'unsafe-eval'; object-src 'none'; base-uri 'none'In plain terms: only scripts that carry the page's one-time nonce run, <object> and <embed> are blocked, and a <base> tag can't redirect relative URLs. Per the file, "Webhook and form pages keep their own sandbox policy and are not affected."
We checked the header on the editor's sign-in page:
| Instance | Header n8n sent |
|---|---|
| 2.45.2, fresh | Content-Security-Policy-Report-Only with the policy above |
| 3.0 nightly (October 22), fresh | Content-Security-Policy with the same policy, enforced |
| 3.0 nightly, upgraded from 2.45.2 | Content-Security-Policy, enforced |
The pull request's title says "on new instances," but the upgraded instance enforced the policy too, so plan for it either way.
Who needs to act: n8n's file says, "If you inject your own scripts into n8n's pages. Test the instance before you update, because a script without the response nonce no longer runs." That covers, for example, analytics or support widgets added to the editor through a reverse proxy. Your options, per the same entry:
- Set
N8N_CONTENT_SECURITY_POLICYto your own policy, or to{}to enforce nothing. - Put a policy in
N8N_CONTENT_SECURITY_POLICY_REPORT_ONLYto try it before you enforce it.
Because 2.x already sends the policy in report-only mode (we checked 2.45.2), you can check today: open the editor with your browser's developer tools and look for CSP violation reports in the console. Anything reported there will be blocked in 3.0.
Workflow tags are always on
N8N_WORKFLOW_TAGS_DISABLED is removed in 3.0. With it set to true, the two versions logged different startup warnings:
# 2.45.2
N8N_WORKFLOW_TAGS_DISABLED -> Disabling workflow tags is deprecated. Tags will always be
enabled in a future version and this environment variable will be removed, so the tags
feature will become visible again after upgrading.

# 3.0 nightly (October 22)
N8N_WORKFLOW_TAGS_DISABLED -> Workflow tags are always enabled. Remove this environment
variable; it is no longer needed.
No data is lost. Per n8n's file, "Tag data was never deleted while the feature was disabled, so tags reappear in the UI and API after the upgrade." Remove the variable, and expect old tags to show up again.
Two more details from n8n's file
- The npm package gets a deprecation notice. "The
n8npackage on npm stays at the last 2.x release and is marked as deprecated." As of October 22, the package isn't marked deprecated yet, which fits a notice that arrives with the release. - Chat Hub's end date. The file says Chat Hub "is deprecated and version 4.0 removes it." In 3.0 it's off by default, and adding
chat-hubtoN8N_ENABLED_MODULESbrings it back for the 3.x line.
Two removals n8n dropped from 3.0
The 3.x branch history also shows changes that were planned and then reverted:
- Execute Sub-workflow "Run once for each item" stays. The removal landed on the 3.x branch in August, and n8n reverted it on October 9. The docs were updated on September 28 to retain the per-item mode.
- The "Any workflow" caller policy stays. Its removal was reverted on September 21, and the entry was taken off the docs page on September 28.
If you started rewriting workflows that call sub-workflows once per item, you can stop.
What to do now
- Keep production on a pinned 2.x version. 2.44.6 is the current stable release; see our n8n 2.45 roundup for what's in beta.
- Check your startup logs. 2.45.2 already warns about
N8N_WORKFLOW_TAGS_DISABLEDand the defaults that change in 3.0. - Look for CSP reports in your browser console if you add anything to n8n's pages.
- Work through the Migration Report and the rest of our n8n 3.0 checklist, which now includes both changes above.
The next weekly release candidate is due on Monday, October 26. We will cover n8n 3.0 on release day in our news section.
Sources
- n8n BREAKING-CHANGES.md on the 3.x branch (n8n on GitHub)
- n8n 3.0 breaking changes (n8n docs)
- feat(core)!: Enforce the default Content-Security-Policy on new instances (n8n on GitHub)
- feat(core)!: Remove N8N_WORKFLOW_TAGS_DISABLED environment variable (n8n on GitHub)
- Developing v3 features (n8n on GitHub)
- n8nio/n8n image tags (Docker Hub)
- n8n package versions and dist-tags (npm)
Editorial team
The then8nblog editorial team researches every article from n8n's release notes, documentation and source code, states the n8n version each guide was tested on, and has every post reviewed by a human editor before it goes live.